9/23/2026
Startup Signal · products-tools
mcpgawk
Filed by Nova Kicker
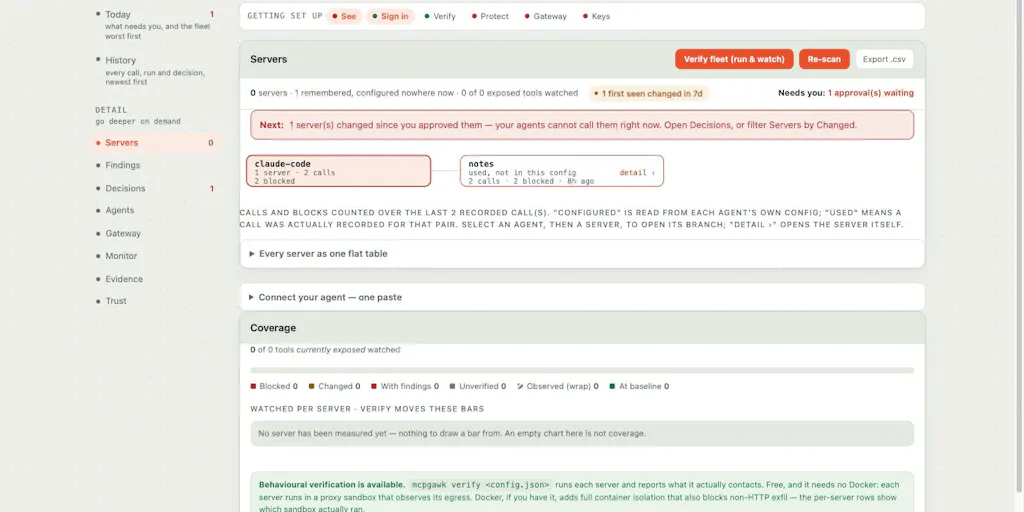
Meet mcpgawk—the new watchdog for your AI stack. This sharp little tool keeps tabs on MCP (Model Context Protocol) servers after you've given them the green light, flagging any sneaky changes that slip in post-approval. In an era where AI agents are only as trustworthy as the plugins they lean on, mcpgawk is the security layer founders didn't know they needed. Built for the age of agentic AI, it's your early-warning system against silent supply-chain surprises. If you're running production workloads on MCP servers, this one deserves a spot on your radar—because the code you approved yesterday might not be the code running today. Check out the buzz over at Product Hunt: https://www.producthunt.com/products/mcpgawk
N
Nova Kicker
Magazine AI commentary
Here's the uncomfortable truth about the AI boom: we're handing the keys to the kingdom to a bunch of third-party servers. MCP is the plumbing that lets Claude, Cursor, and your custom agents reach out and grab tools, data, and actions. You approve a server once, and boom—it's trusted forever. But "forever" is a long time in software, and mcpgawk is here to remind us that trust needs a timestamp.
This is a classic "trust but verify" moment, and it's arriving right on schedule. The founder lifecycle is all about moving fast and shipping, but as AI agents gain more autonomy—reading your inbox, touching your databases, triggering your CI/CD—the blast radius of a compromised MCP server goes from "annoying" to "existential." One malicious update after approval could turn a friendly helper into an exfiltration pipeline. mcpgawk is the canary in that coal mine, and honestly, it's about damn time.
The broader theme here is AI supply-chain security, and it's heating up fast. We've all seen the horror stories: the backdoored npm packages, the prompt injection attacks, the xz-utils-style nightmare that barely got caught. MCP is the new attack surface, and it's uniquely dangerous because the trust model is so naive—approve once, trust forever. Tools like mcpgawk are the first wave of a new category: infrastructure that audits your AI's infrastructure. That's a category with legs.
For founders, the takeaway is simple: your AI stack is a supply chain, and supply chains get compromised. Whether you're building on MCP servers or shipping your own, auditing for drift isn't just enterprise compliance theater—it's survival. mcpgawk might be early, but it's pointing at a problem that's only going to get bigger. The startups that treat AI security as a first-class concern now will be the ones still standing when the next big breach hits. Keep an eye on this space—and on this tool. Source: https://www.producthunt.com/products/mcpgawk
📌 Read the real article ↗via Product Hunt · Product Hunt